Category Archives: Blog
LLMjacking and the Developer Blind Spot
Two major incidents in October 2026 began on developer systems. Our CTO, Barry Rooney, explains [...]
20
Nov
Nov
OT security: The devices nobody is watching
Supermarket fridge attacks in Ireland, France and Sweden have shown how exposed operational technology has [...]
02
Nov
Nov
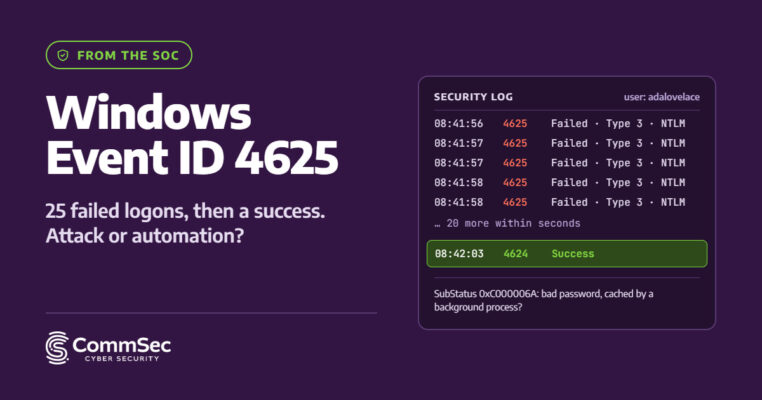
Windows Event ID 4625 Failed Logons
Twenty-five failed logons followed by a success looks like a brute-force attack. Often, it is [...]
23
Oct
Oct
Passkeys explained: why they are more secure than SMS and voice MFA
SMS and voice codes can be phished, intercepted or relayed in seconds, and Microsoft is [...]
07
Oct
Oct
Security Quick Wins to Finish the Year Strong
It has been a big year for IT teams. If there is any fuel left [...]
05
Oct
Oct
Cyber Resilience Act: What Irish Software Firms Must Do
The Cyber Resilience Act now covers software sold in Europe. Reporting rules started on 11 [...]
30
Sep
Sep
Not Every Security Check Needs a Full Penetration Test
CVE volume keeps breaking records, yet the flaws that actually get exploited are old, patchable, [...]
23
Sep
Sep
Do You Still Need Active Directory? AD vs Entra ID
Many organisations are quietly running two identity systems at once, legacy on-premises Active Directory and [...]
26
Aug
Aug

OWASP LLM Top 10: What It Means Alongside the Web App Top 10
OWASP has released its Top 10 for LLM Applications 2026, led by Steve Wilson and [...]
07
Aug
Aug

Penetration Testing and Compliance: What DORA, NIS2, CyFun, NIST and ISO 27001 Actually Require
Every major framework asks the same question in different words: can you prove your controls [...]
14
Jul
Jul